Automated CycloneDX
SBOM Generation Tool
Generate accurate CycloneDX SBOMs from source code, natively integrated into DerScanner's SCA platform.
Produce auditable, machine-readable Software Bills of Materials. Identify transitive dependency risks. Meet SBOM transparency requirements outlined in EO 14028 and the EU Cyber Resilience Act, without slowing down production builds.
Why Your Team Needs DerScanner SBOM Generator?
CycloneDX SBOM across 12 ecosystems.
Generates SBOMs in JSON for Java, JavaScript, Python, Go, Swift, and 8 other ecosystems. Output is ready for audit, procurement, and compliance workflows.
Full transitive dependency coverage
Captures direct dependencies along with every layer beneath. Hidden components that supply chain attackers exploit show up in the inventory by default.
Native CVE and license overlay
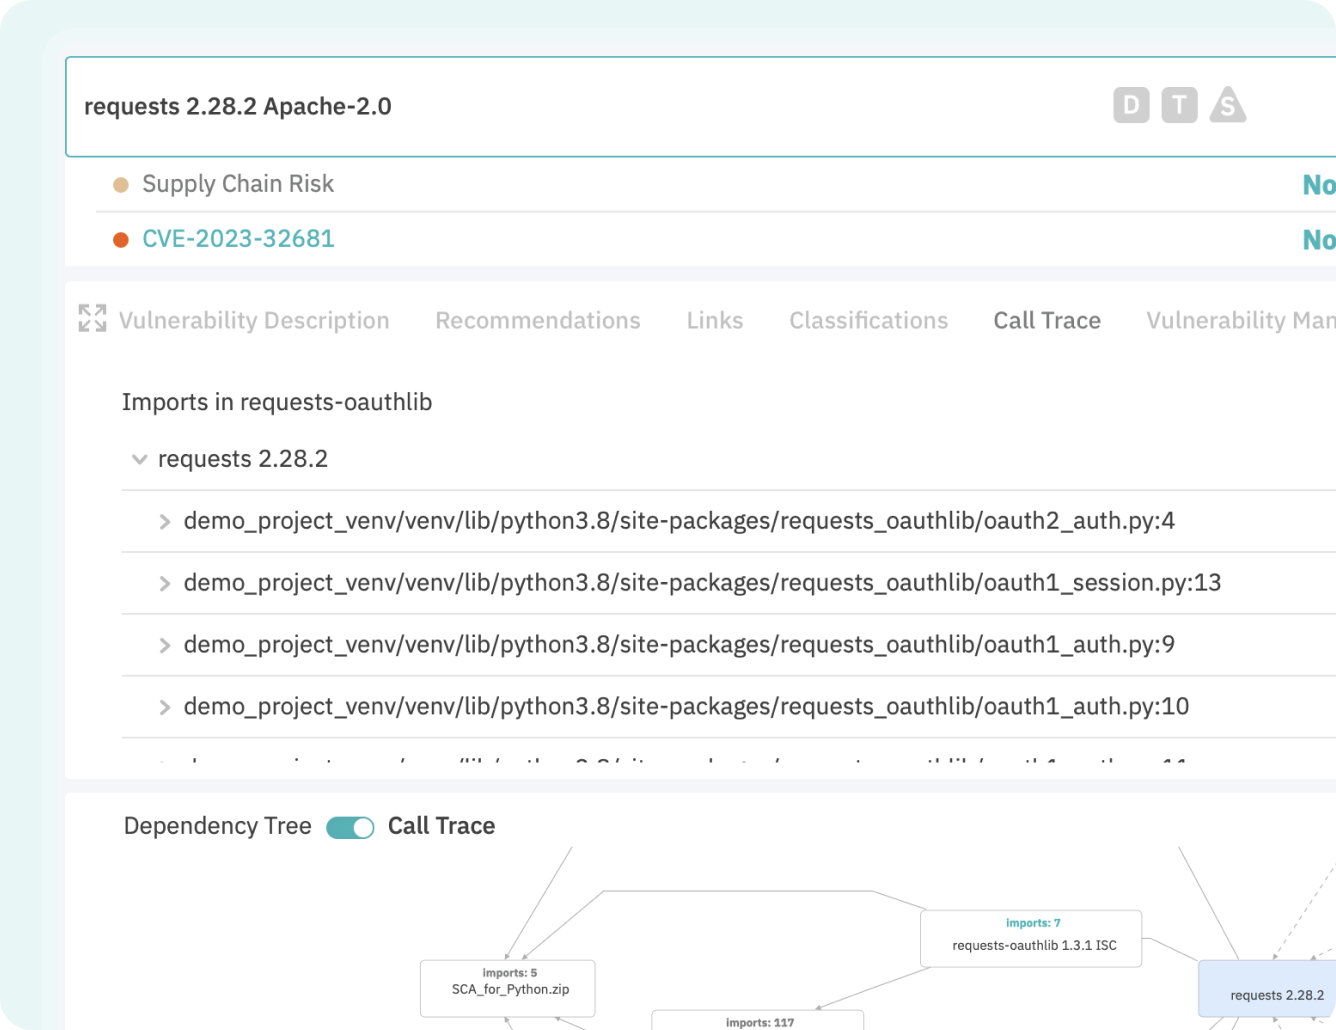
Every SBOM component is automatically cross-referenced against NVD, GitHub, GitLab, OSV, and proprietary vulnerability data, plus license metadata for policy enforcement.
CI/CD pipeline integration
Generate fresh SBOMs on every build through Jenkins, GitLab CI, Azure DevOps Server, TeamCity, or CLI. Keep the inventory up to date as dependencies change.
Why Modern Companies need Automated SBOM Generation

U.S. Executive Order 14028
It establishes SBOM transparency expectations for software sold to federal agencies, with implementation guided by NIST SSDF.

EU Cyber Resilience Act (CRA)
It imposes legal accountability and component-tracking requirements on manufacturers of products with digital elements. CycloneDX SBOMs and continuous monitoring provide the technical foundation for these obligations.

Incident response
Without an SBOM, it takes days of grepping across repos to understand if the codebase is affected by the new vulnerability. With one, it takes minutes. Automated SBOM generation turns incident response from a fire drill into a query.

The cost of inaction
Open-source supply chain attacks have grown dramatically, and breaches involving third-party components carry some of the highest remediation costs in the industry.
Key Capabilities
for Software Supply Chain Security
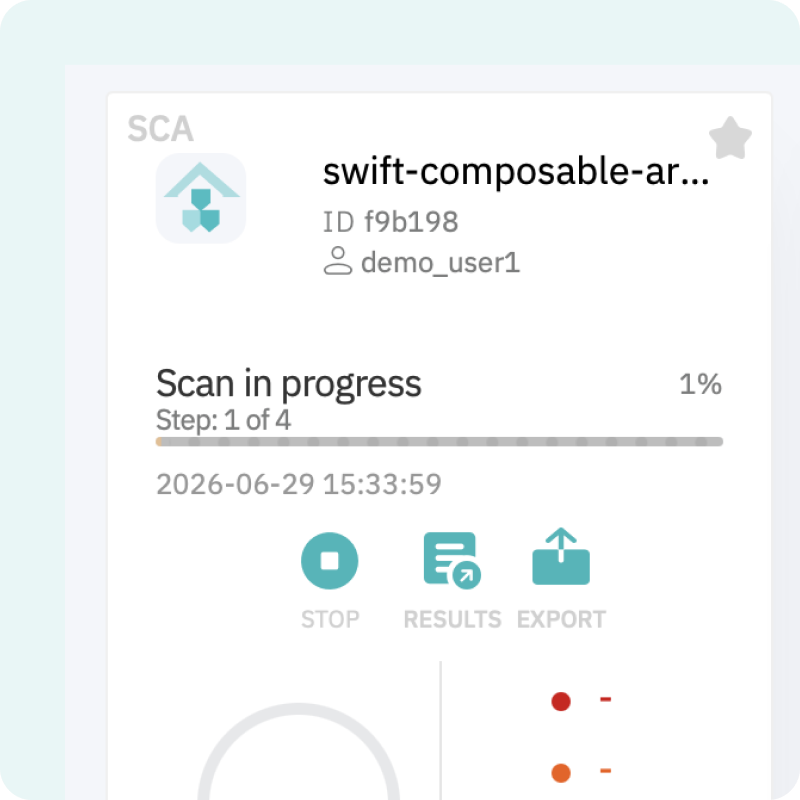
Automated SBOM creation during builds
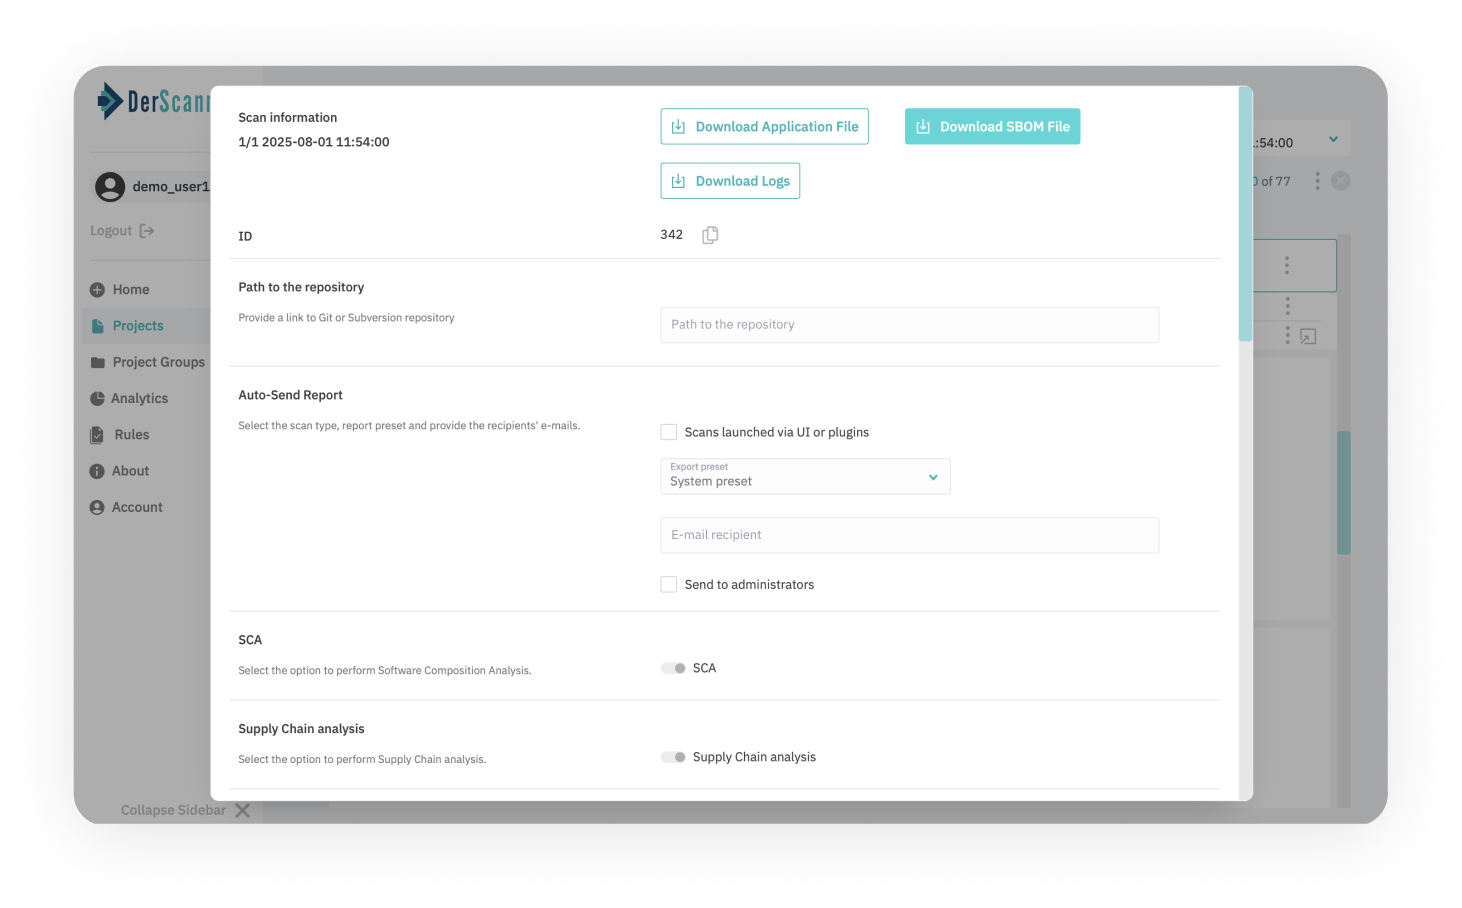
Generate CycloneDX SBOMs continuously during builds, deployments, and release processes through Jenkins, GitLab CI, Azure DevOps Server, TeamCity, or CLI. The inventory stays up to date as dependencies change.
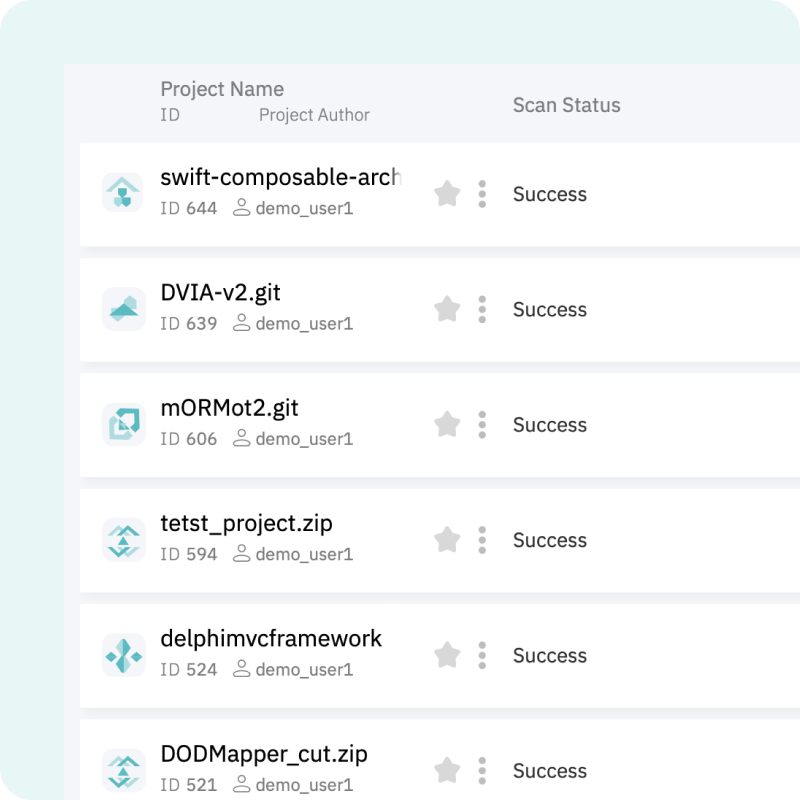
Multi-ecosystem support
Generate SBOMs for JavaScript/TypeScript, PHP, Python, Ruby, C#/VB.NET, C/C++/Objective-C, Go, Java/Kotlin/Scala, Rust, Swift, and Erlang. Coverage includes major package managers like npm, pip, Maven, Gradle, NuGet, Cargo, Composer, Go modules, CocoaPods, and Swift Package Manager.
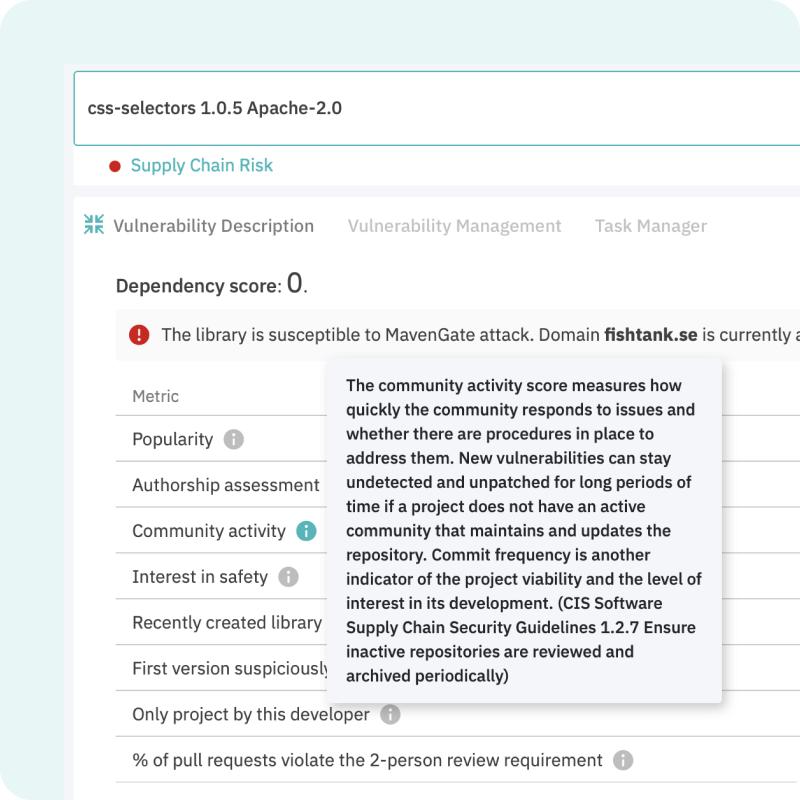
Vulnerability and license overlay
Every SBOM component is automatically cross-referenced against known CVEs and license metadata. Findings appear in the same inventory the SBOM is generated from, so security and procurement teams work from one source of truth instead of stitching together separate reports.
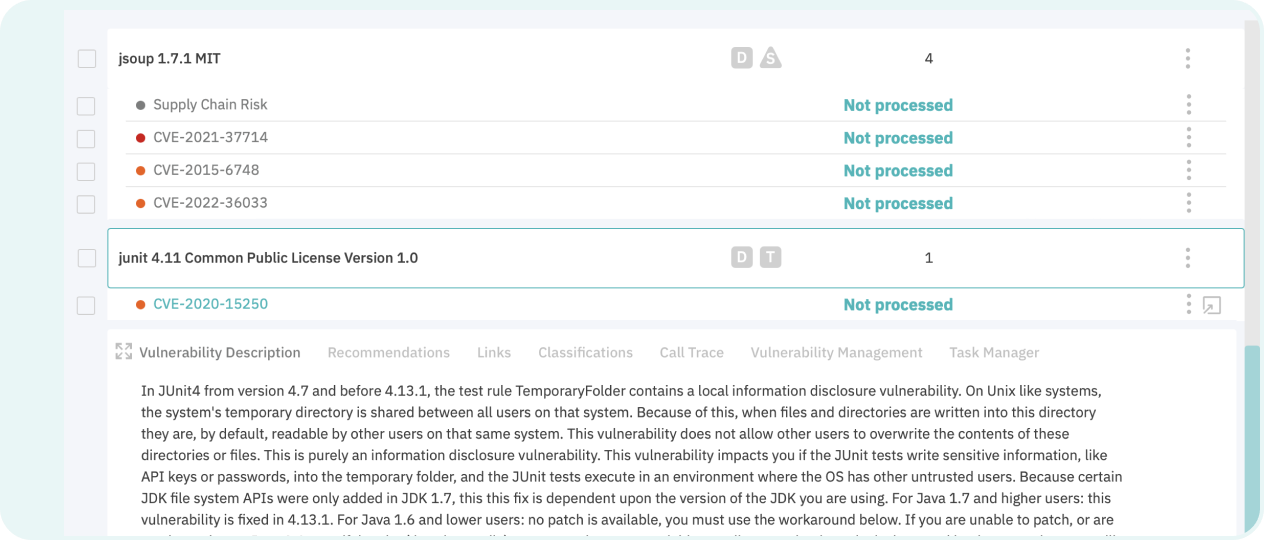
Every component in the output carries the data security and compliance teams need:
- Package name, version, and ecosystem
- Direct vs transitive dependency relationship
- License metadata
- Linked CVEs from NVD, GitHub, GitLab, OSV, and DerScanner's proprietary datasets
- Component fingerprint for traceability
- Supplier and source repository where available
Continuous monitoring
SBOMs should be generated per release. DerScanner tracks newly disclosed vulnerabilities in deployed dependencies, surfacing new risks against components that were clean at release time on each scan.
Approved by industry leaders
The Static Application Security Testing Landscape, Q2 2023
The Software Composition Analysis Landscape Q2 2024
The Static Application Security Testing Solutions Landscape Q2 2025


What Is SBOM
Generation?
A Software Bill of Materials (SBOM) is a formal, machine-readable inventory of every component inside a piece of software: every open-source library, third-party package, and dependency, including the dependencies of your dependencies. The SBOM acts as a full ingredient list for your application.
SBOM generation is the process of producing that inventory automatically by scanning your codebase or build artifacts. Done properly, the process captures what your developers intentionally included along with every transitive dependency layered beneath, the hidden components that supply chain attackers most often exploit.
Manual dependency tracking is slow and incomplete. DerScanner automatically generates accurate CycloneDX SBOMs from source code, helping your team reduce supply chain risk, meet emerging regulatory requirements, and secure every dependency across the SDLC.
Frequently Asked Questions
Generate Your First SBOM Today
Sign up for a personalized demo to see how DerScanner can meet your SBOM and compliance requirements