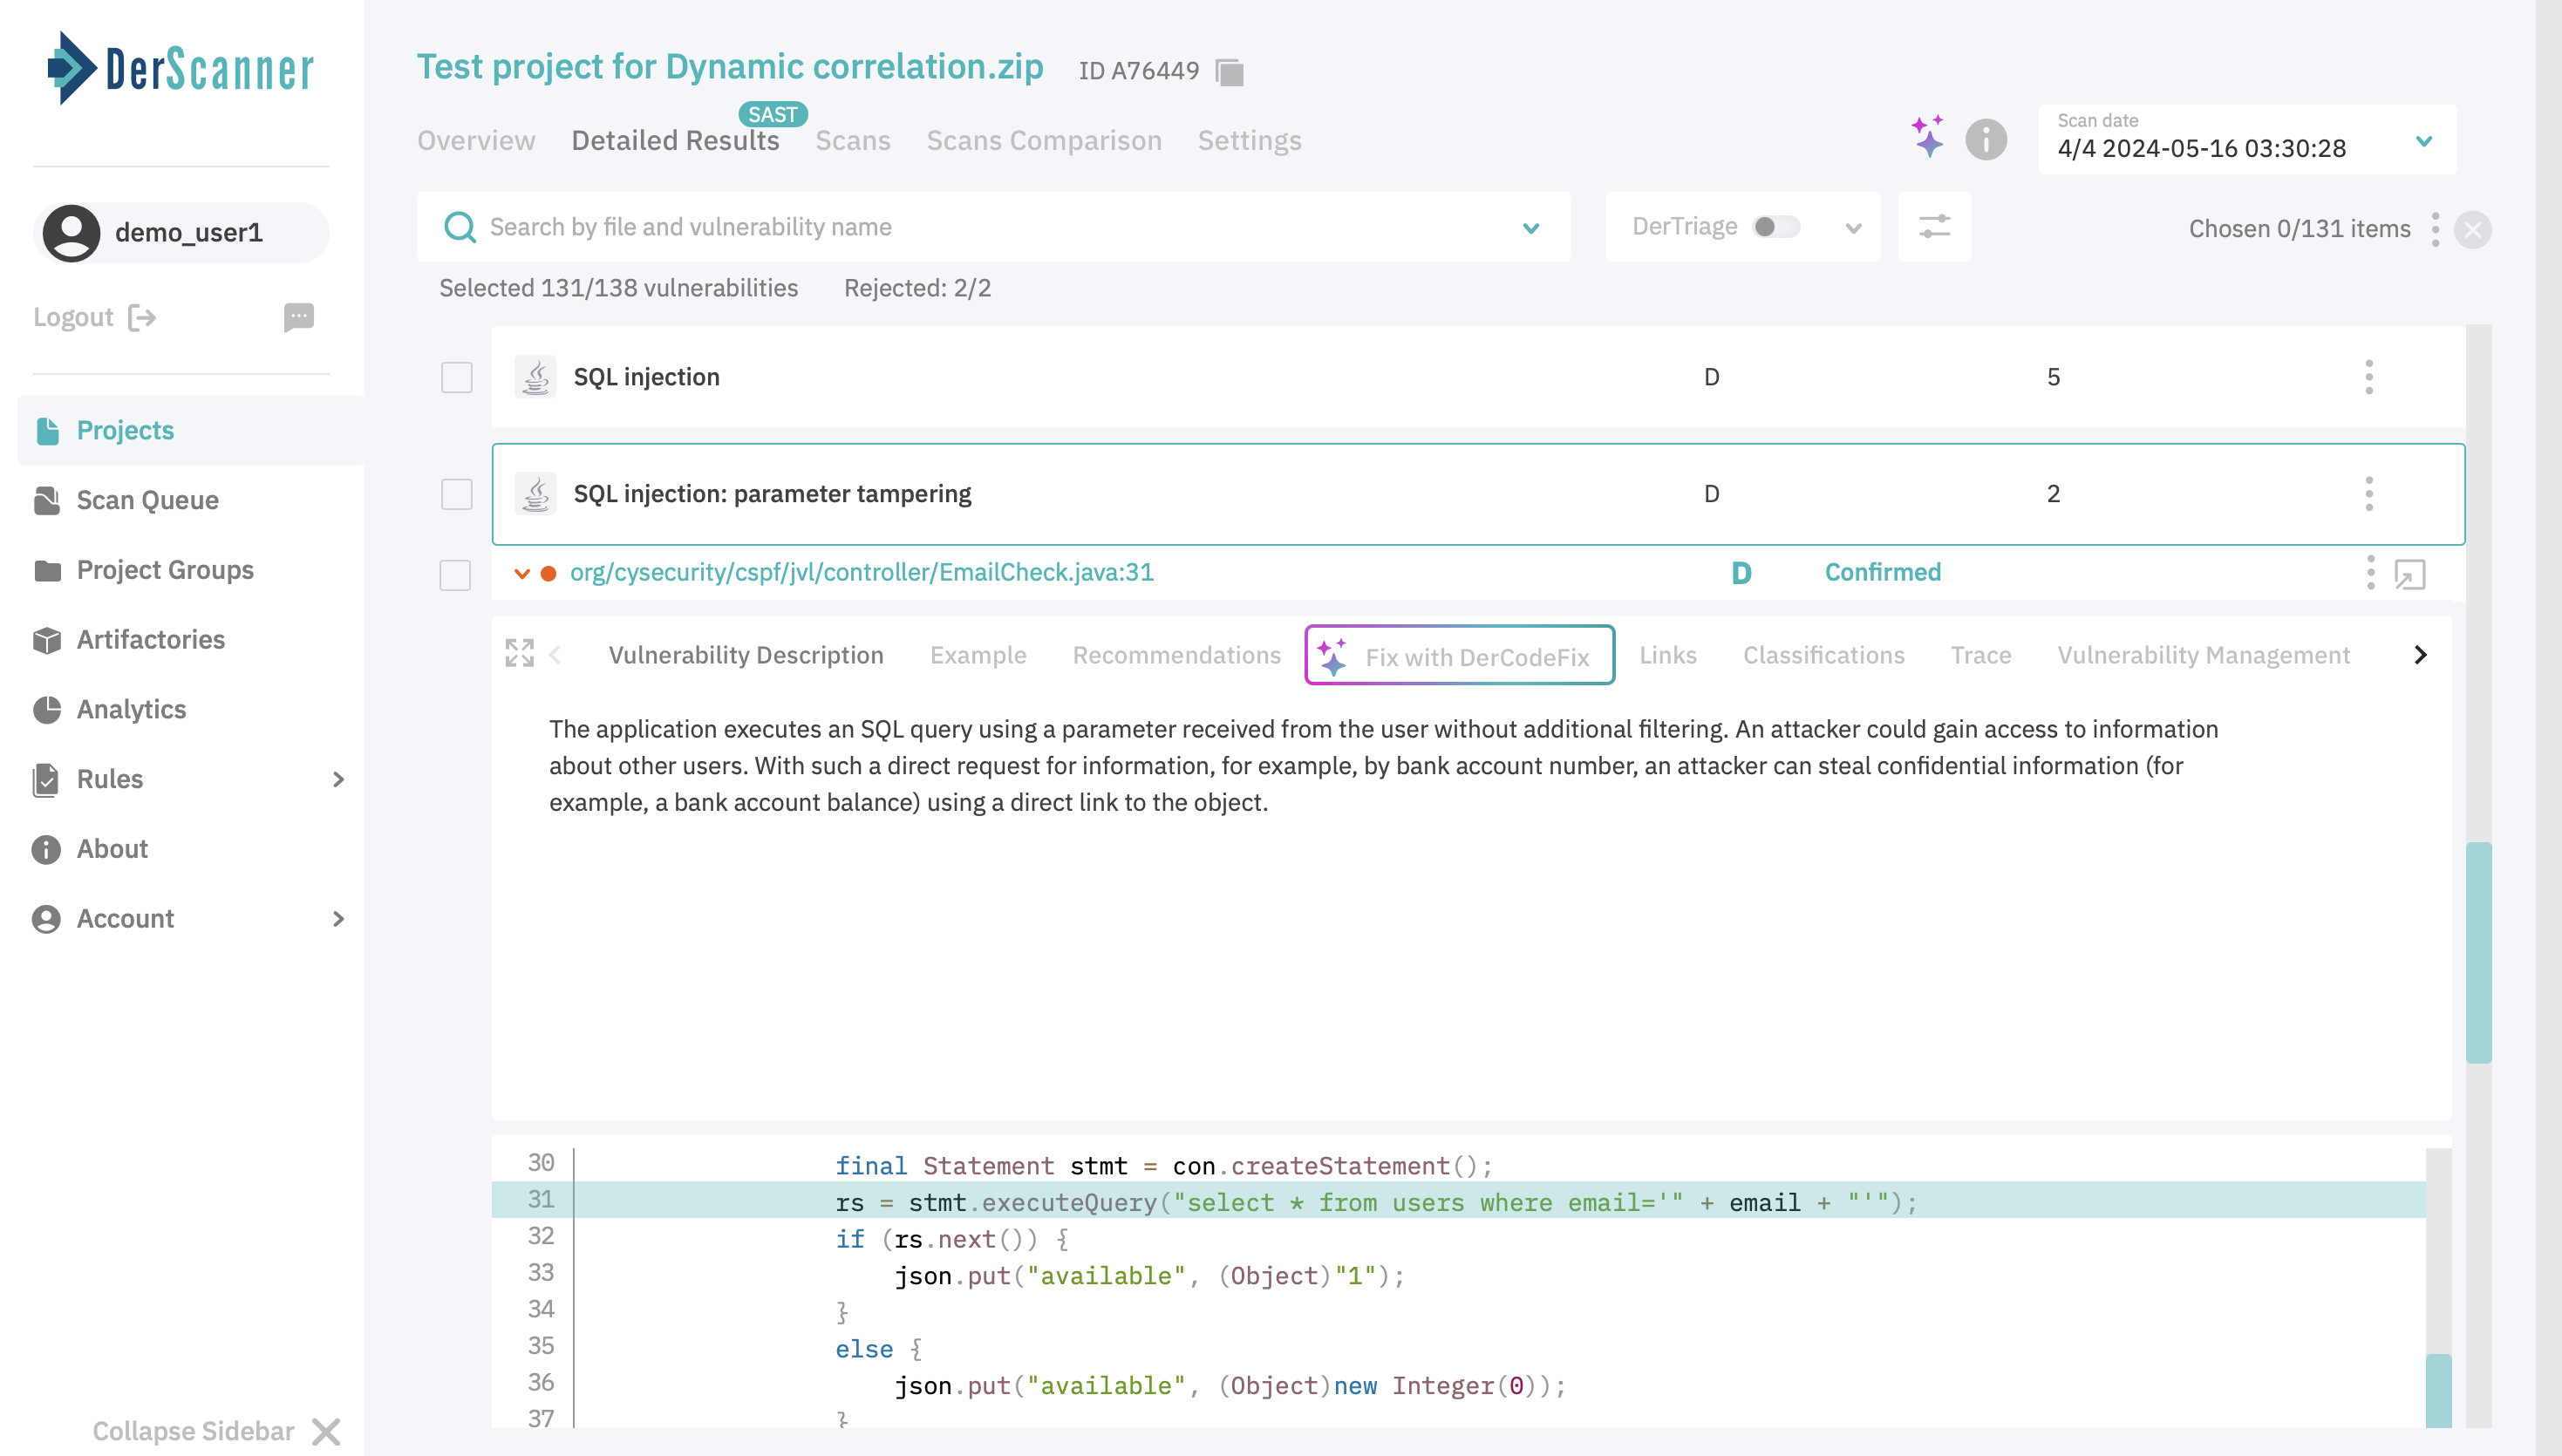
Fix first
Put confirmed findings at the top of the backlog
SAST findings confirmed by dynamic analysis are marked in Detailed Results. The team starts with the marked findings.
of findings are both severe and highly exploitable
Veracode SoSS 2026
year-over-year rise in high‑risk vulnerabilities
Veracode SoSS 2026
of breaches start with an exploited vulnerability
Verizon DBIR 2026
to fix a high or critical application flaw
Edgescan 2026
Securing the world's best teams

Fix first
SAST findings confirmed by dynamic analysis are marked in Detailed Results. The team starts with the marked findings.
Setup
Up to date
Each SAST scan correlates with the latest completed DAST scan. After a new DAST scan, rescan the SAST project to refresh the marks.
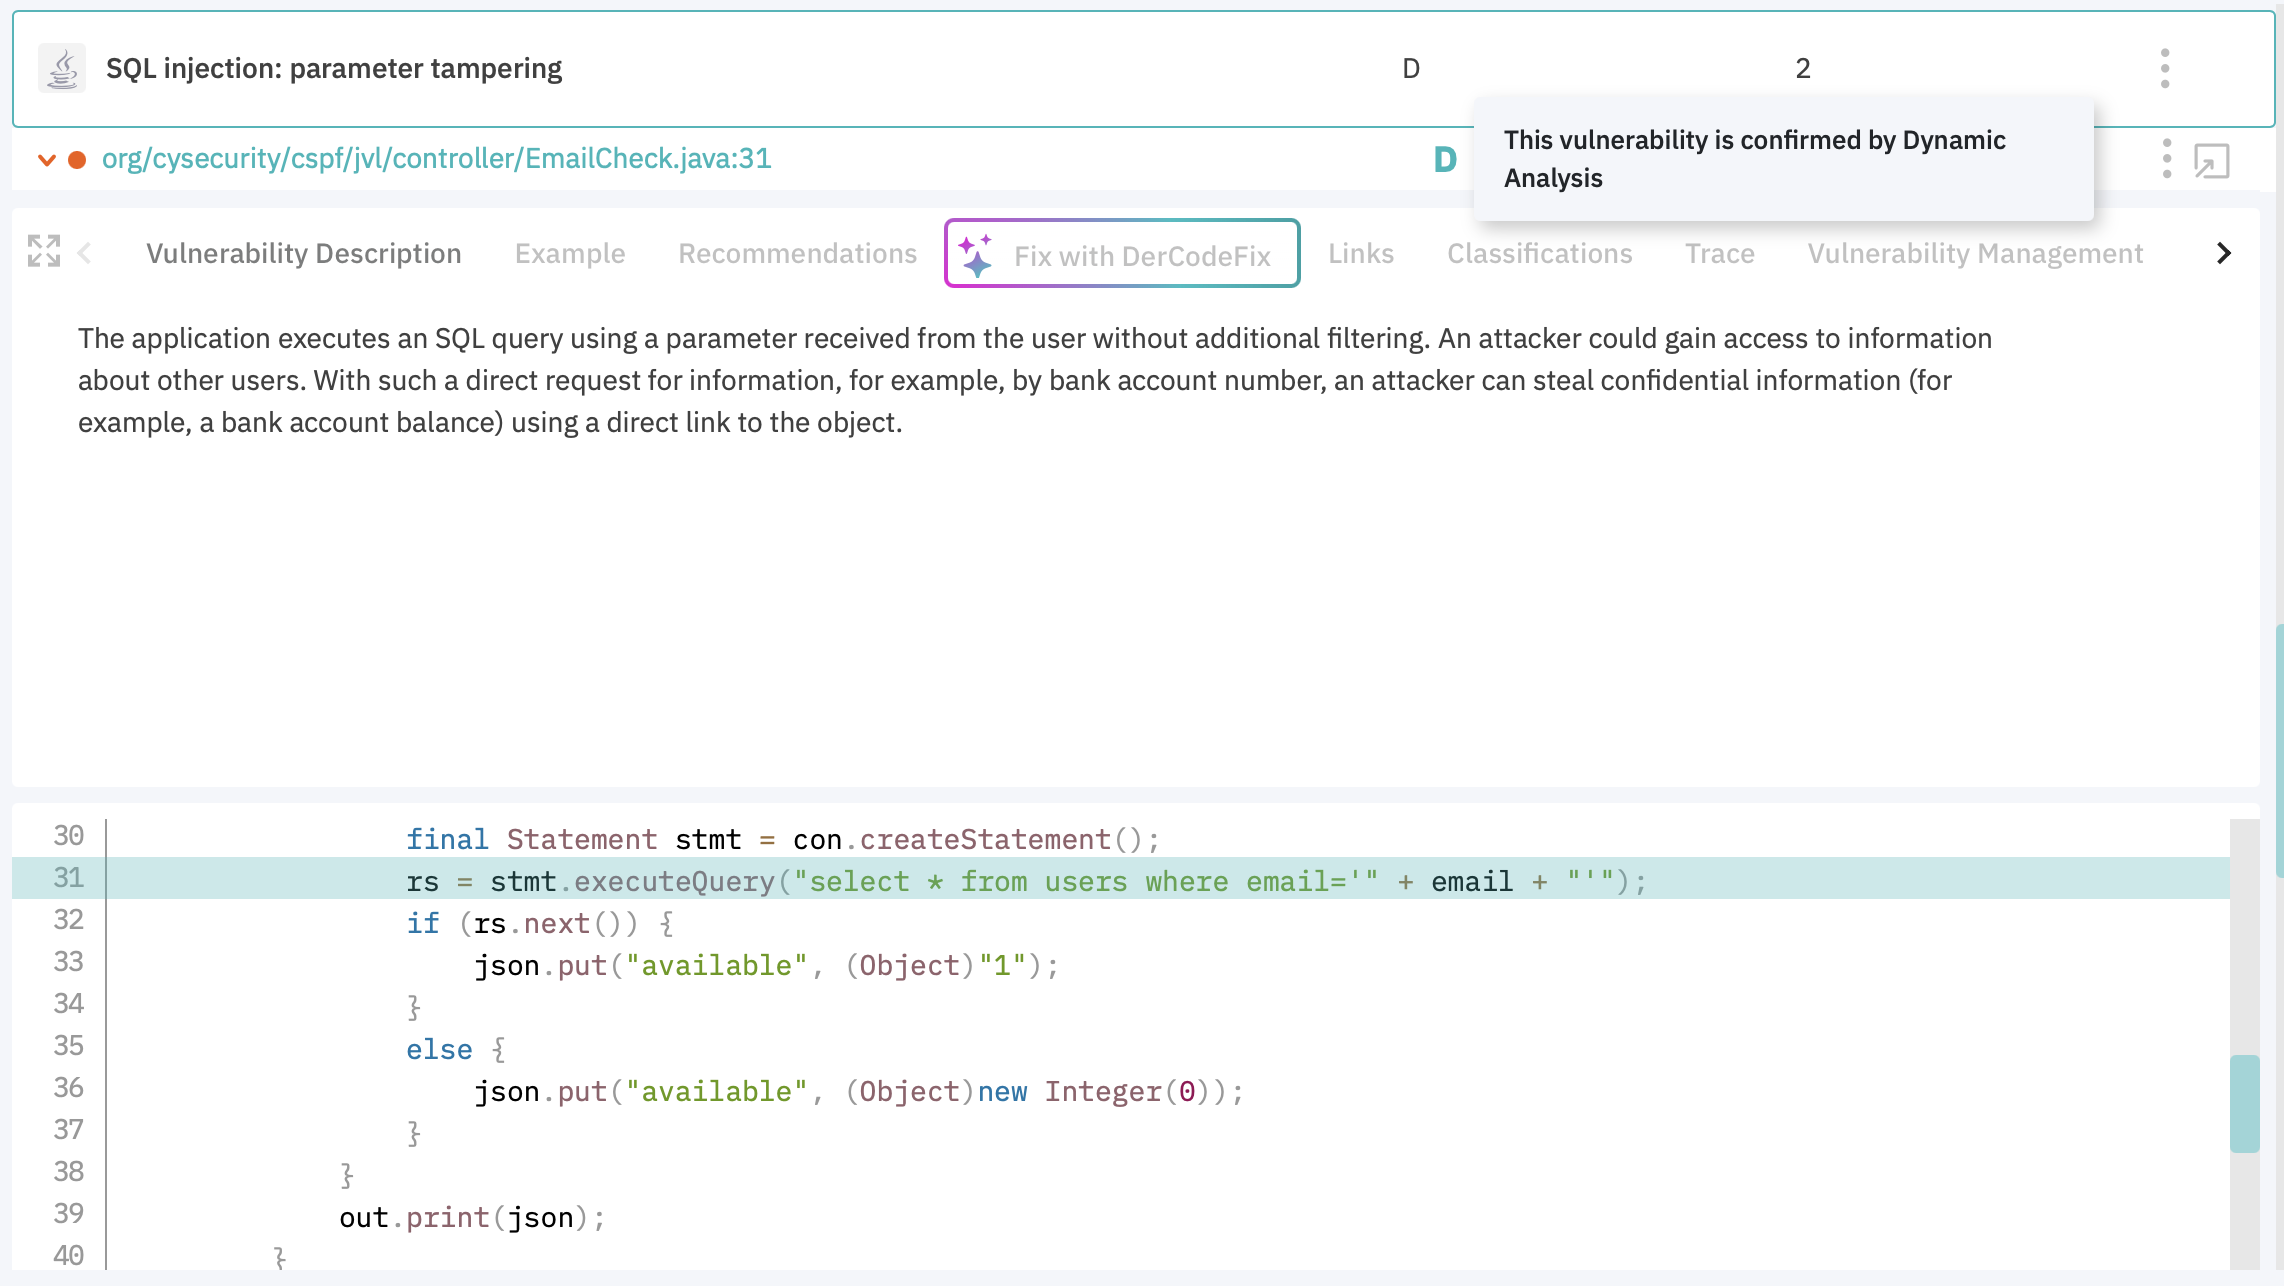
Proof for developers
SAST points to the place in the code. The mark shows that dynamic analysis of the running application confirmed the same vulnerability type.
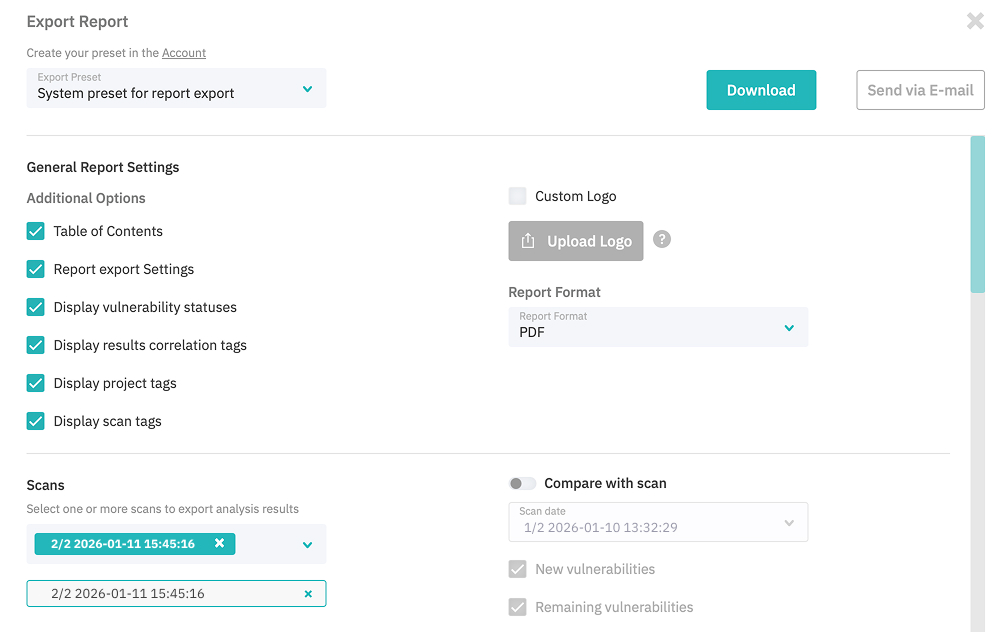
Audit evidence
Turn on "Display results correlation tags" in the report settings, and the SAST report marks every finding confirmed by DAST.
Inside the network
DerScanner installs on-premise, including air-gapped networks. Source code, application URLs and results stay on internal servers.
When looking for the scanner to build our secure development process on, we evaluated the capabilities of global leading vendors. We were surprised with the very convenient licensing model along with the capabilities of the product. DerScanner addresses our main challenge of checking the health of our product's code.
We use DerScanner to support our secure code review and SAST services. Its broad language support, reliable static analysis, and actionable findings help our consultants deliver consistent, high-quality security assessments.
Interactive application security testing combines the views of static and dynamic analysis. Classic IAST places an agent inside the running application and watches code execute during tests. DerScanner takes a different route: it correlates the results of a SAST scan and a DAST scan of the same application, and tags the static findings confirmed by dynamic analysis.
Agent-based IAST runs inside the application runtime and depends on test traffic reaching the instrumented code. DerScanner installs nothing in the application: it matches findings from two independent scans. This fits environments where security policy does not allow agents in the application or on its servers. The result is a SAST finding list with confirmed vulnerabilities tagged, ready for prioritization.
SAST reads source code and points to the place of a flaw before the application runs. DAST tests the running application from the outside, with no access to the code. IAST joins both views. In DerScanner, SAST findings whose vulnerability type the DAST scan confirmed are marked, so the code location and the dynamic confirmation appear in one list.
The same application needs a SAST project for its source code and a DAST project for its running web version. After at least one completed DAST scan, open New scan settings in the SAST project, select the DAST project under "Correlate results with DAST findings" and start the scan. Correlation uses the last completed scan of the DAST project.
No. Correlation marks SAST findings whose vulnerability type dynamic analysis confirmed, and leaves the rest of the list in place for review. For the rest of the static findings, the AI agent DerTriage verifies each detection and marks it Confirmed or Rejected, with the reasoning attached to the finding.
Yes. In the General report settings of the SAST project, turn on "Display results correlation tags". The exported report then marks every finding confirmed by dynamic analysis, so auditors and managers can separate confirmed vulnerabilities from the rest of the static findings.
Yes. DerScanner installs on-premise, including air-gapped networks, and both scans run inside the perimeter. Source code, application URLs, credentials and results stay on internal servers.
Prefer email? company@derscanner.com